Optimizely Malware Hit 178 Organisations In One Day, Report URI Finds
Optimizely malware reached 178 organisations on Nov 16, 2026, swapping crypto addresses and skimming cards. See the full timeline and the open questions.
Optimizely malware was deployed onto the visitors of 178 firms on 16th November 2026. This piece of information has been released by Report URI, which specializes in providing web security services. According to Scott Helme of this company, attackers had managed to insert malicious code into customer projects on the Optimizely Web testing platform.
Where the malware sat inside Optimizely snippets
Report URI blog post by Scott Helme on the Optimizely malware, dated November 16, 2026. Source: Report URI.
Optimizely Web works in a fairly straightforward way. The customers get a JavaScript file from Optimizely's content delivery network. This file has a Project JavaScript field that contains any custom code written by the customers. The attacker used this Project JavaScript field to inject the short loader into it for many unrelated customers. There was no modification in other parts of the file, so it remained accessible from cdn.optimizely.com with Optimizely's certificate.
The study conducted by Report URI identified 1,611 distinct snippets, 188 of which are infected and belong to 178 businesses. Some of them include Zoom, BBC, CNN, Salesforce, GitLab, IKEA, HSBC, Equifax, Air France-KLM and Ledger. In the words of Helme, the true count is probably higher because the team could only check the snippets it had found. Six crypto trading companies were identified as having been compromised by the attack. Yet another frontend hijack was discovered in the Across domain hijack report.
The payload did four jobs in one script
All the capabilities that come with the Optimizely malware were incorporated into the one file known as track.js. The address switcher in the code will detect all the valid addresses pertaining to Bitcoin, Ethereum, EVM chains, Tron, Solana, TON, Litecoin, Bitcoin Cash, and Dogecoin. This code will first validate the checksum before it can replace any of the addresses.
Skimming software was installed at 13:43 UTC. The software will search for the credit card number, expiry date, and security code in the forms. Credit cards input using payment forms hosted via Stripe or Adyen were inaccessible to the card skimmer software. The ones input via the site were accessible.
The same script, whenever it made a swap, was uploading the cookies and page screenshots to the malicious server during the process. It loads exploit kits, including Coruna and DarkSword, when running on iPhone and iPad devices. According to the Report URI, Coruna and DarkSword have been patched on iOS 18.7.3 and newer, iOS 26.3 and newer.
Optimizely malware timeline and the money taken
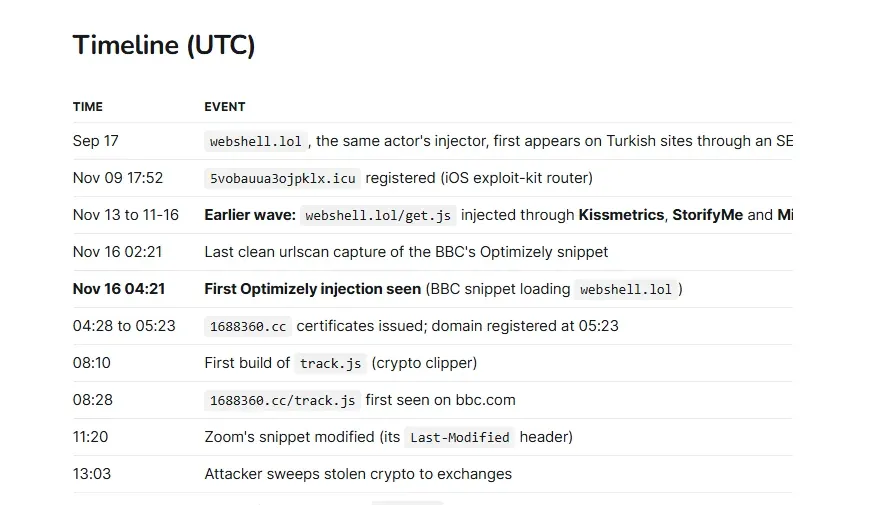
Timeline table from the Report URI post, with times in UTC. Source: Report URI.
The first injection was found at 04:21 UTC in the BBC snippet. Track.js first appeared on bbc.com at 08:28 UTC. Report URI detected the mass clean-up around 20:40-21:10 UTC, while Ledger snippet was cleaned at 20:41. By 21:52 UTC, only one snippet from a total of 188 remained containing the malicious code, which belonged to TalkTalk.
As of 19:25 UTC on November 16, the attacker's addresses had received about $7,040 in about nine hours. About 0.08298 BTC accounted for $5,380 in the total amount. Sweeping the funds was carried out between 13:03 and 13:05 UTC. According to Report URI, it is not possible to estimate how many cards or cookies were harvested by the attacker.
What is still unknown
Report URI is not aware of how the attacker gained write access to all those customer projects. The optimizely.com and login.optimizely.com scripts were also loaded with the malicious code. The firm says it contacted Optimizely and had received no response when it published. Sites that use the platform should search every project for 1688360.cc and for the atob( function.
Everyone who entered the crypto destination within the period of the Optimizely malware attack must check each and every character before sending funds.
Related News
Ankr Bridge Exploit Drained Five Tokens In 144 Seconds
Ankr bridge exploit drained five tokens in five Ethereum transactions over 144 seconds, and the bridge was paused 1 hour 42 minutes later, chain data shows.
Aave V3.8 Proposal Adds A Reentrancy Guard To 15 Deployments
The Aave V3.8 proposal adds a transient-storage reentrancy guard for 15 Aave V3 deployments. See the rollout list, licence terms, audits and next steps.
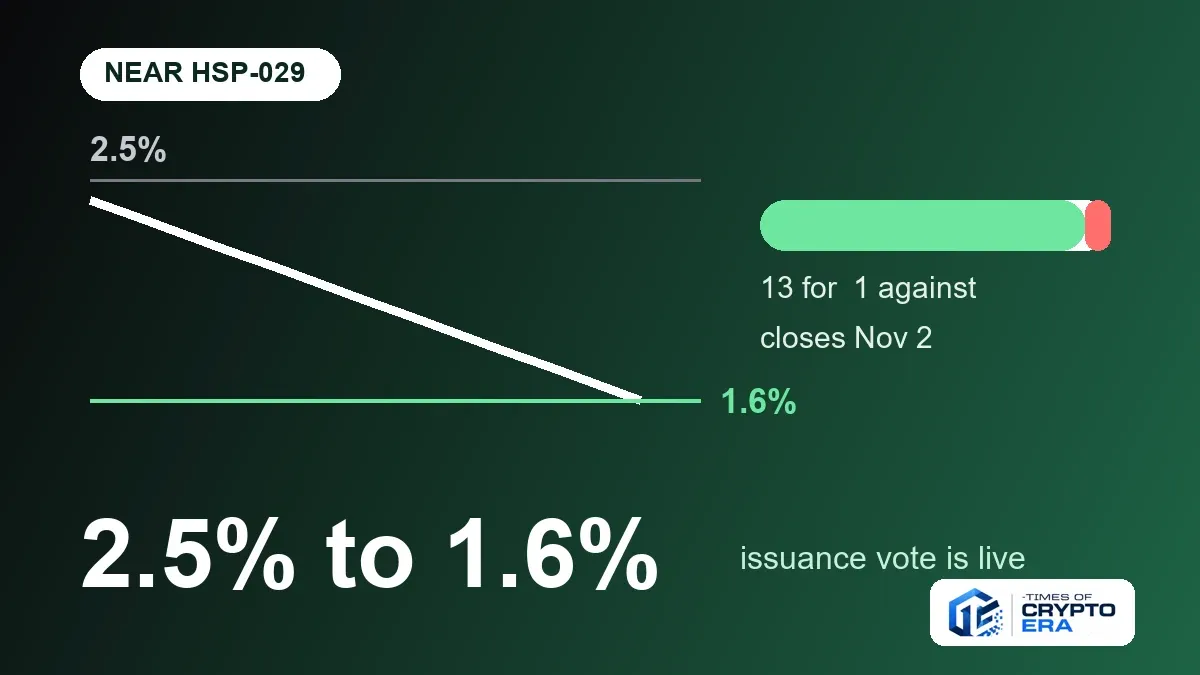
NEAR Issuance Cut To 1.6% Is Live In A House Of Stake Vote
The NEAR issuance cut in HSP-029 would lower maximum issuance from 2.5% to 1.6% over 24 months. The House of Stake vote closes November 2 at 4:48 pm UTC.
Tether Revenue Reaches $20.59B On DefiLlama, $117.7M In 7 Days
Tether revenue stands at $20.586B on DefiLlama, with $117.67M in 7 days and $17M in 24 hours, while USDT supply fell 4.4% in a month. See how it is counted.