Cardano Linux Flaw: Ubuntu Fixes Land, Three Old Releases Lag
Cardano Linux flaw CVE-2026-98432 now has fixed Ubuntu kernels for four current releases, while 20.04, 18.04 and 16.04 stay vulnerable on the Nov 11 tracker.
The Cardano Linux flaw reported by Intersect to the stake pool administrators on October 30 now has fixed kernels for all four currently supported Ubuntu versions. The status of CVE-2026-98432 on the Canonical website was updated on November 11, 2026. Three older Ubuntu versions are still marked as vulnerable, with work in progress.
Intersect wrote the Weekly Update #135 while Ubuntu was among those distributions that had not issued a patch yet. The recommendation made back then was contingent upon something. It is that operators be advised to install the corrected kernel and reboot the machine after the distribution has done that. Now is the time for Ubuntu users to do just that.
What the Cardano Linux flaw is and who runs the affected machines
CVE-2026-98432 is considered to be critical by Ubuntu. Its CVSS score is 9.8. From the Ubuntu tracker, it is known that this vulnerability is in the handling of IPv4 TCP connections in the Linux kernel and allows for remote code execution. The kernel code describes a use-after-free bug in the function ip_options_build.
Stake pools are servers and servers have kernels. Intersect instructed operators to check which kernel their block producer and relays are running. Block producers are those servers where the signature process occurs. Relays are the nodes which interact with other parts of the network.
The Intersect notice is quite concise. It mentions that there was a critical vulnerability in the Linux kernel which affected a number of distributions, among which there was Ubuntu, and that some distributions already had the fix while some did not.
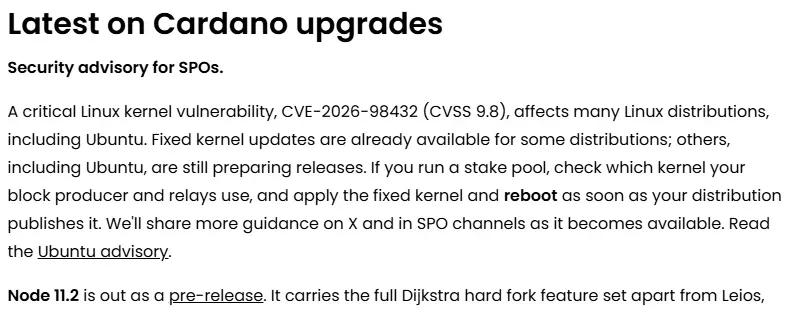
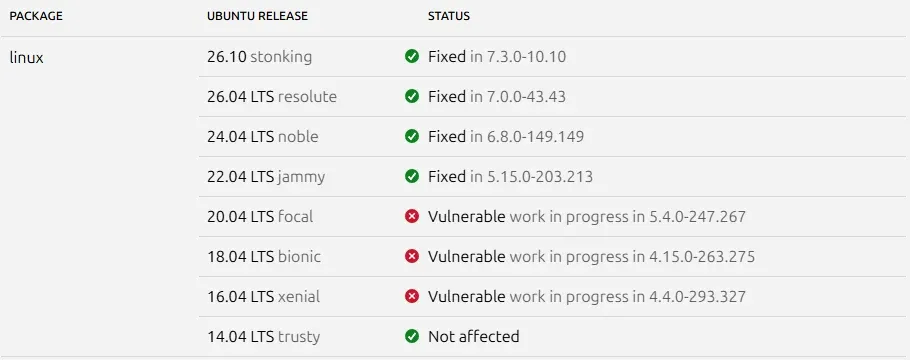
Top: Security advisory from Intersect’s Weekly Update #135. Bottom: Status table from the CVE-2026-98432 page of Ubuntu, last updated on November 11, 2026. References: Intersect, Weekly Update #135 and Ubuntu CVE-2026-98432.
The Ubuntu status table, line by line
The table above includes a fixed kernel for each currently released Ubuntu version. The fixed versions of Ubuntu 26.10, 26.04 LTS, 24.04 LTS, and 22.04 LTS are 7.3.0-10.10, 7.0.0-43.43, 6.8.0-149.149, and 5.15.0-203.213, respectively.
There are three other old Ubuntu versions that have a different tag: vulnerable. The updates for these Ubuntu 20.04 LTS, 18.04 LTS, and 16.04 LTS are still in progress with the kernel versions being 5.4.0-247.267, 4.15.0-263.275, and 4.4.0-293.327, respectively. Ubuntu 14.04 LTS is not affected.
An operator on a fixed release is left with two tasks: to install the new package and to restart the machine, as only after a reboot can the new kernel be executed. The tracker needs to be monitored by anyone using 20.04 or older, since the fix versions are still listed as work in progress.
A quick check for operators and delegators
Patching the kernel is not all there is in the schedule of maintenance activities. The same announcement from Intersect talks about the release of Node 11.2 in pre-release form with the full Dijkstra hard fork features except for Leios. Operators on DijkstraNet have to upgrade before the hard fork on the testnet, so fixing the Cardano Linux flaw sits right beside another upgrade.
Kernel status can be seen with one command, that is, uname -r. In case the kernel is less than the fixed version for the release, then rebooting the machine is necessary after the update process. Delegators can verify the pool status by looking at the announcements and blocks on the explorer.
Featured image: Server Room by Carl Lender, licensed CC BY 2.0, via Wikimedia Commons.
Related News
Robinhood CEO Stock Sale: Tenev Sold 375,000 Shares in October
Robinhood CEO stock sale: Tenev sold 375,000 shares on October 5 under a 10b5-1 plan. The Form 4 shows zero direct Class A but 47.4M Class B still held.
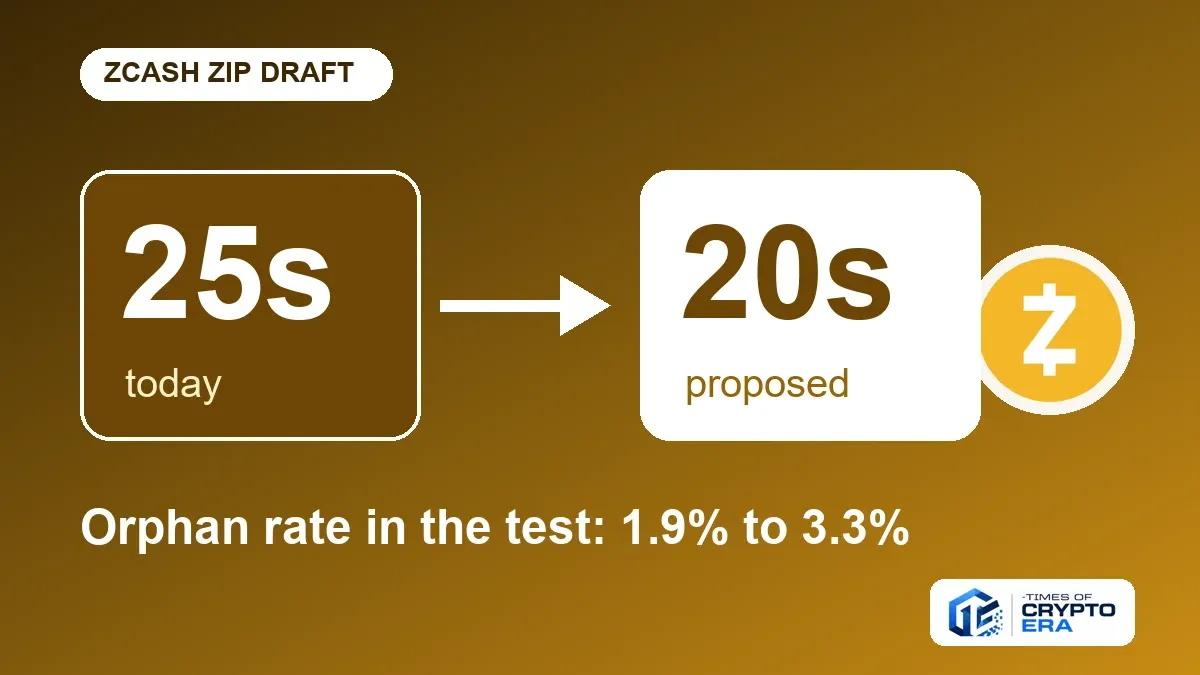
Zcash Block Time Draft Cuts 25 Seconds To 20 After NU7
Zcash block time would fall from 25 to 20 seconds under a draft ZIP posted November 8, with tests showing orphan rates of 1.9% to 3.3% on full 2 MB blocks.
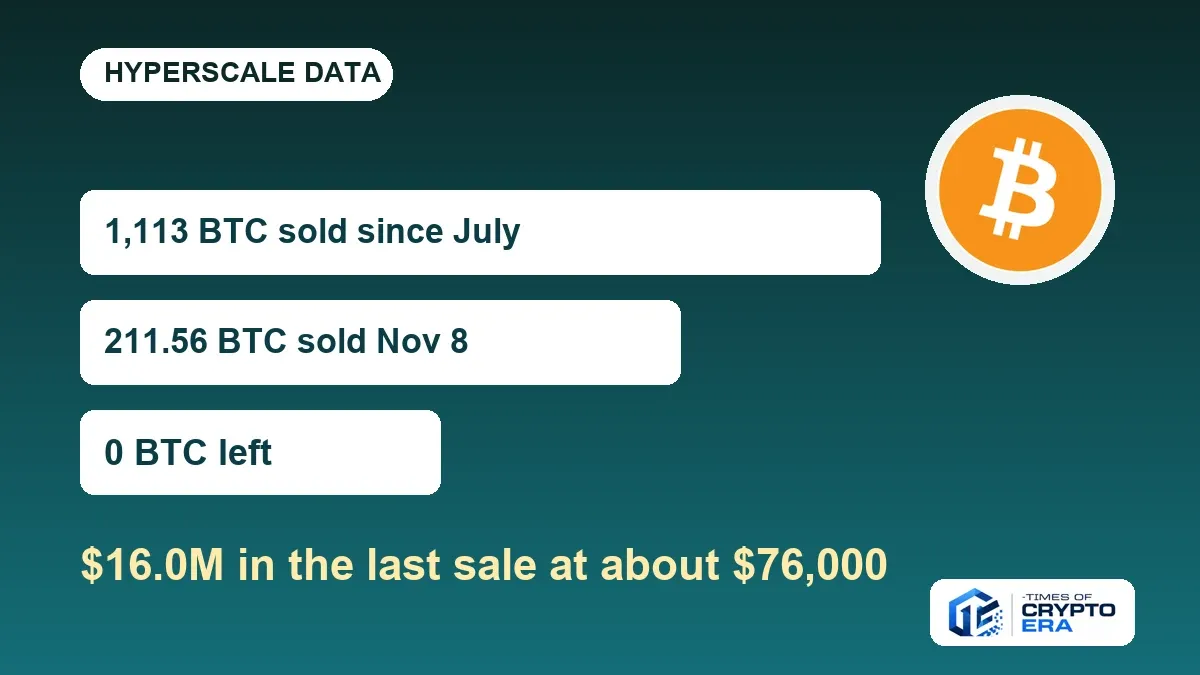
Hyperscale Data Bitcoin Sale Ends At 211.56 BTC And $16M
Hyperscale Data bitcoin sale ended November 8 with 211.56 BTC sold near $76,000, and an 8-K shows $27 million convertible note package signed two days earlier.
Evernorth Merger Closes With XRP Priced At $1.43, Not $2.37
The Evernorth merger closed October 9 with XRP priced at $1.43069, down 39.5% from signing. See the 8-K share math, lock-up terms and trust redemptions.