Phala Cloud Attack: Post-Mortem Shows 17.5 Hours Before Detection
Phala Cloud attack post-mortem: attacker read some customers' logs and secrets for hours before detection. Here is what Phala says was and wasn't reached.

In this article+
The Phala Cloud attack went unnoticed for about seventeen and a half hours, according to Phala's own post-mortem. The company published it on October 19, a week after its automated checks caught the intrusion. The report explains how an attacker read some customers' logs and secrets, and what Phala says was never touched.
What the attack reached
The Phala Cloud attack started with a flaw. Phala says an attacker exploited it in the dstack guest-agent between October 8 and October 12. The agent handles management and attestation inside each Confidential VM. A request path in the logs feature accepted a crafted container name and handed it to the Docker API without checks. That turned a log request into a container-inspect call, which returned configuration including environment variables.
Environment variables are where many apps keep secrets. Phala says it sent every affected customer a notice listing the exact applications, time windows and data volumes. Those customers are told to rotate whatever secrets sat in their environment variables.
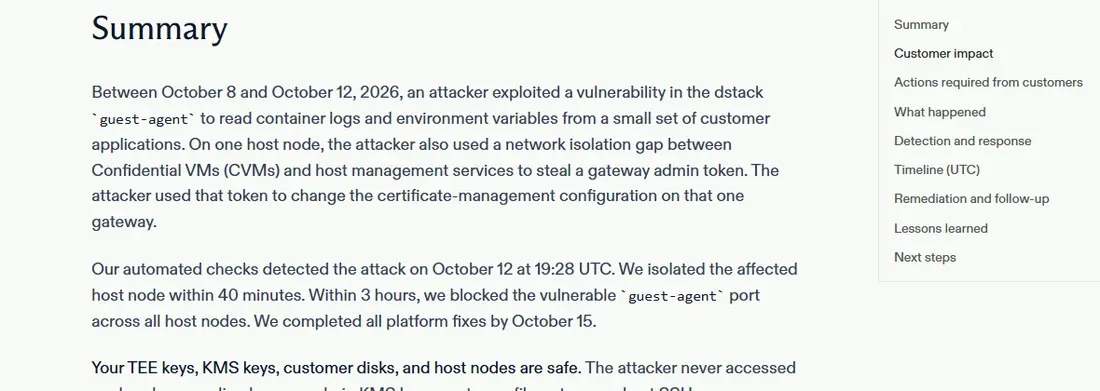
The summary at the top of Phala's October 19 post-mortem. Source: Phala post-mortem.
How one host node was used to go further
On one host node the attacker did more. According to the report, code running inside a customer app that accepts user code scanned the host's internal network. It reached a management API that needed no login and changed firewall rules. The attacker then used the guest-agent flaw against the gateway container and obtained a gateway admin token.
That token made 63 changes to DNS-credential and ACME settings on one gateway between October 11 and October 12. Phala says active certificates stayed valid and issuance never stopped. It also says it replaced the Cloudflare DNS token with an IP-restricted one the same day.
What Phala says stayed safe
The post lists what it says was not reached. TEE keys and the key management service returned zero bytes to unauthorized requests on every node. Customer disks were not readable, and nobody got SSH or a remote shell on a host node. The on-chain key management on Base and Ethereum was upgraded and re-attested on October 14.
The company admits several of its own mistakes. Gateways shared one admin token, and the console template switched public logs on by default. Security logs were kept for only seven days. A tenant machine should never have been able to reach host management ports at all, the post says.
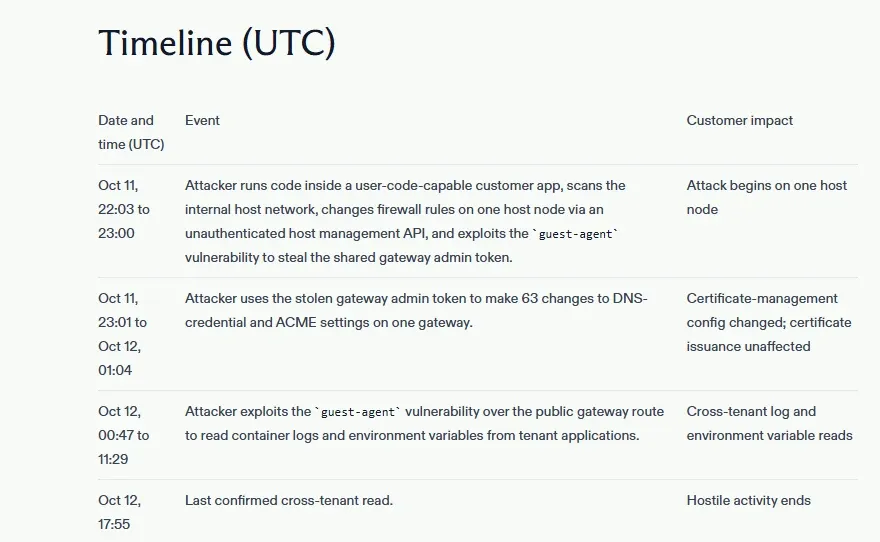
Part of the timeline table in the post-mortem. Source: Phala post-mortem.
The upgrade deadline for Phala Cloud customers
Fixed releases are dstack v0.6.1 and v0.5.12. Customers have until November 19 to move to one of them. From November 20 Phala will upgrade the rest in batches. Each batch gets at least 24 hours' notice on the status page. Machines on v0.3.x images will be retired that day. Enterprise plans are excluded from that retirement.
The PHA price on the same day
The token traded very differently on October 19. PHA opened near $0.048 and touched $0.0697 before closing at $0.0622. About 203.5 million tokens changed hands, against roughly 20 million on a quiet day that week. It was still near $0.064 on October 20.
The post-mortem went live the same day, but nothing we found connects the two. Phala's report does not discuss its token at all, and the Phala Cloud attack it describes ended on October 12.
Loading…
Written by
Daniel Kiprop covers exchanges, listings, stablecoins and institutional crypto moves for Times of Crypto Era. Stories start from company filings and official announcements, not secondary coverage.
View full profile →Related News

Spark Risk Curation Vote: Curators Could Cut Risk Without A Poll
Spark risk curation vote SAEP-24 would let curators cut caps without a poll. It runs to October 22 beside a ratification of a Safe that differed from its poll.

OSMO Price Analysis: A $0.0649 Sweep Fades On A 138M-Token Day
OSMO price analysis: a $0.0649 sweep on October 19 faded to $0.0543 on 138.4M tokens. Levels, two Osmosis votes and four-hour scenarios for the next move.

Visa Mesh Stablecoin Spending: 175M Locations, But No Launch Date
Visa Mesh stablecoin spending would reach 175 million merchants, per Mesh's October 19 release. No platform, launch date or device list has been named yet.